
FIOR AI Gateway Enables Singapore Financial Institutions to immediately comply with MAS AI risk rules
News originally published by
EIN Presswire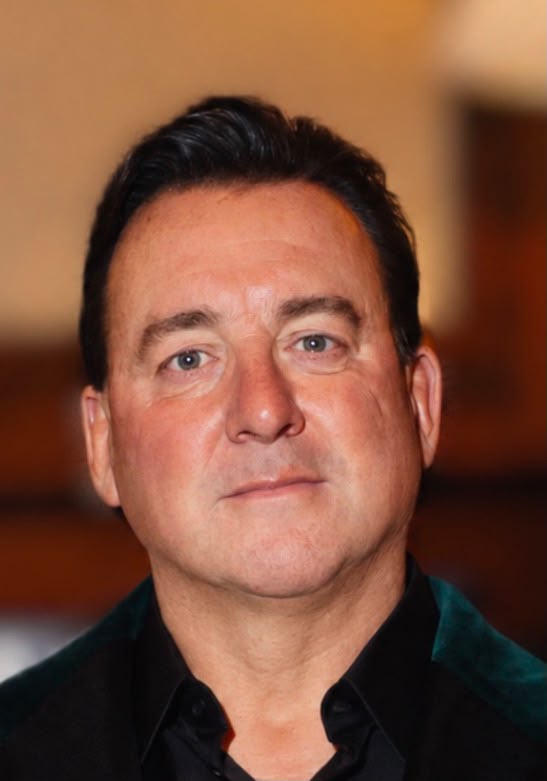
David Williams, Founder, FIOR

Quantum Safe Self Sovereign AI Identity and Enforcement
FIOR AI Gateway maps its controls to the MAS Guidelines on AI Risk Management
We believe sovereignty is critical – Financial Institutions should not allow agents to put value at risk without certainty that their Identity cannot be compromised.”
SINGAPORE, SINGAPORE, November 16, 2026 /EINPresswire.com/ -- FIOR, the identity and enforcement layer for AI, today published a product analysis to demonstrate how financial institutions can use the FIOR AI Gateway to immediately comply with the requirements of the Monetary Authority of Singapore’s (MAS) Guidelines on Artificial Intelligence Risk Management.— David Williams, Founder, FIOR
Exhibiting at the Singapore Fintech Festival on the UK Government pavilion, FIOR will show financial institutions how easily they can put secure, sovereign, enforceable, auditable controls around their AI agents well before the Guidelines take effect.
MAS issued the final Guidelines on 7 October 2026. They apply proportionately to all financial institutions and to all forms of AI, including generative AI and AI agents, covering board oversight, AI inventories, risk assessment and life cycle controls. Oversight and inventory expectations apply from 7 October 2027, and life cycle controls from 7 October 2028.
FIOR’s AI Gateway installs in under an hour within an institution’s own environment. It sits between AI agents and the models and tools they use, gives each agent a cryptographic identity, checks every request against the institution’s own policies before it can act, and records every decision in a tamper-evident audit trail. Unapproved models and tools are refused by default, personal data can be masked, unregistered “shadow AI” is flagged, designated agent actions can be held for human approval, and a compromised agent can be revoked across the whole fleet. Identities are protected by NIST standard post-quantum cryptography. The FIOR system is self-sovereign, so no data needs to leave the enterprise boundary in order to create an agentic identity.
The mapping covers 74 paragraphs and sub-paragraphs of the Guidelines and sets out, for each, what FIOR enforces, what it evidences and what remains the institution’s own decision. FIOR operates the control for 14, shares responsibility for 32 and supports a further 28 that sit with the institution’s board and senior management. The detailed document can be reviewed at https://fior.group/resources/.
FIOR’s AI Gateway has been successfully “NCSC CRTF Cyber Resilience Assessed” under the UK National Cyber Security Centre’s (NCSC) Principle Based Assurance scheme, with all 72 of FIOR’s security claims for the product assessed as met. In a May 2026 Vendor Profile, industry analyst IDC described FIOR as “a differentiated player in the rapidly evolving AI security landscape”.
The launch comes as Singapore’s regulators turn their attention to AI agents that can carry out financial tasks. In July, MAS and industry partners published the Safeguards for Agentic Finance at Runtime (SAFR) white paper, and this month MAS’ Future of Finance Institute began operations, including to support implementation of the new Guidelines. Tomorrow (19 November), MAS, the UK’s Financial Conduct Authority and American Express will debate accountability for AI agents on the festival’s Policy Stage.
David Williams, Founder and CEO of FIOR, said:
“Singapore has set a clear and practical standard for how financial institutions should govern AI, and it rightly covers AI agents as well as models. The hard part is turning those expectations into secure and sovereign controls that operate on every agent action and producing evidence a supervisor will accept. Institutions can install FIOR’s AI Gateway in under an hour, use the existing MAS policy pack and also set their own policies. From that point, they know which agent is acting, what it is allowed to do and have a tamper-evident record of every decision.
“We believe sovereignty is critical – Financial Institutions should not allow agents to put value at risk without certainty that their Identity cannot be compromised, and with FIOR they do not have to send secret data about the existence and activity of agents outside the enterprise boundary in order to generate an identity.
We are delighted to be back in Singapore with the UK Government delegation this week and look forward to working with financial institutions here as they prepare for 2027.”
FIOR is exhibiting at the Singapore FinTech Festival at Singapore EXPO from 18 to 20 November 2026, on the UK Government pavilion.
ENDS
NOTES TO EDITORS
About FIOR
FIOR is the identity and enforcement layer for AI.
FIOR’s AI Gateway enables organisations to identify AI agents and tools, determine what each agent is authorised to do and enforce those permissions before actions are executed.
Designed to operate across organisational and technology boundaries, FIOR provides cryptographic identity, deterministic policy enforcement, rapid revocation and tamper-evident audit capabilities.
FIOR’s patent-pending deterministic identity technology is not only cryptographically secure (using NIST standard quantum resistant cryptography, it is also self-sovereign). All of the identity processes are carried out inside the enterprise boundary by the FIOR software. No information leaves the enterprise and no data needs to be sent to an identity provider.
https://fior.group
Media contacts
Henry Lerwill and Francesca Eaton
Hawthorn Advisors | fior@hawthornadvisors.com
* FIOR’s AI Gateway is NCSC CRTF Cyber Resilience Assessed having been evaluated (PBA-004, report issued 9 November 2026) against 18 NCSC principles across five themes: secure design and development; build environment security; secure deployment and maintenance; communication with customers; and product-specific usage, design and operation. All 72 claims were met. Assessment conducted via an NCSC Cyber Resilience Test Facility (CRTF) does not imply compliance with regulatory standards, best practice, or any other form of certification.
David Williams
Fior Group Limited
Visit us on social media:
LinkedIn
Legal Disclaimer:
EIN Presswire provides this news content "as is" without warranty of any kind. We do not accept any responsibility or liability for the accuracy, content, images, videos, licenses, completeness, legality, or reliability of the information contained in this article. If you have any complaints or copyright issues related to this article, kindly contact the author above.
